Introduction
Autobase is an Internal Database Platform for PostgreSQL, bringing the managed database experience of DBaaS into your own infrastructure. Create and manage hundreds or thousands of production-ready, highly available PostgreSQL clusters.
This solution is tailored for use on dedicated physical servers (recommended), virtual machines, and within both on-premises and cloud-based infrastructures.
Architecture
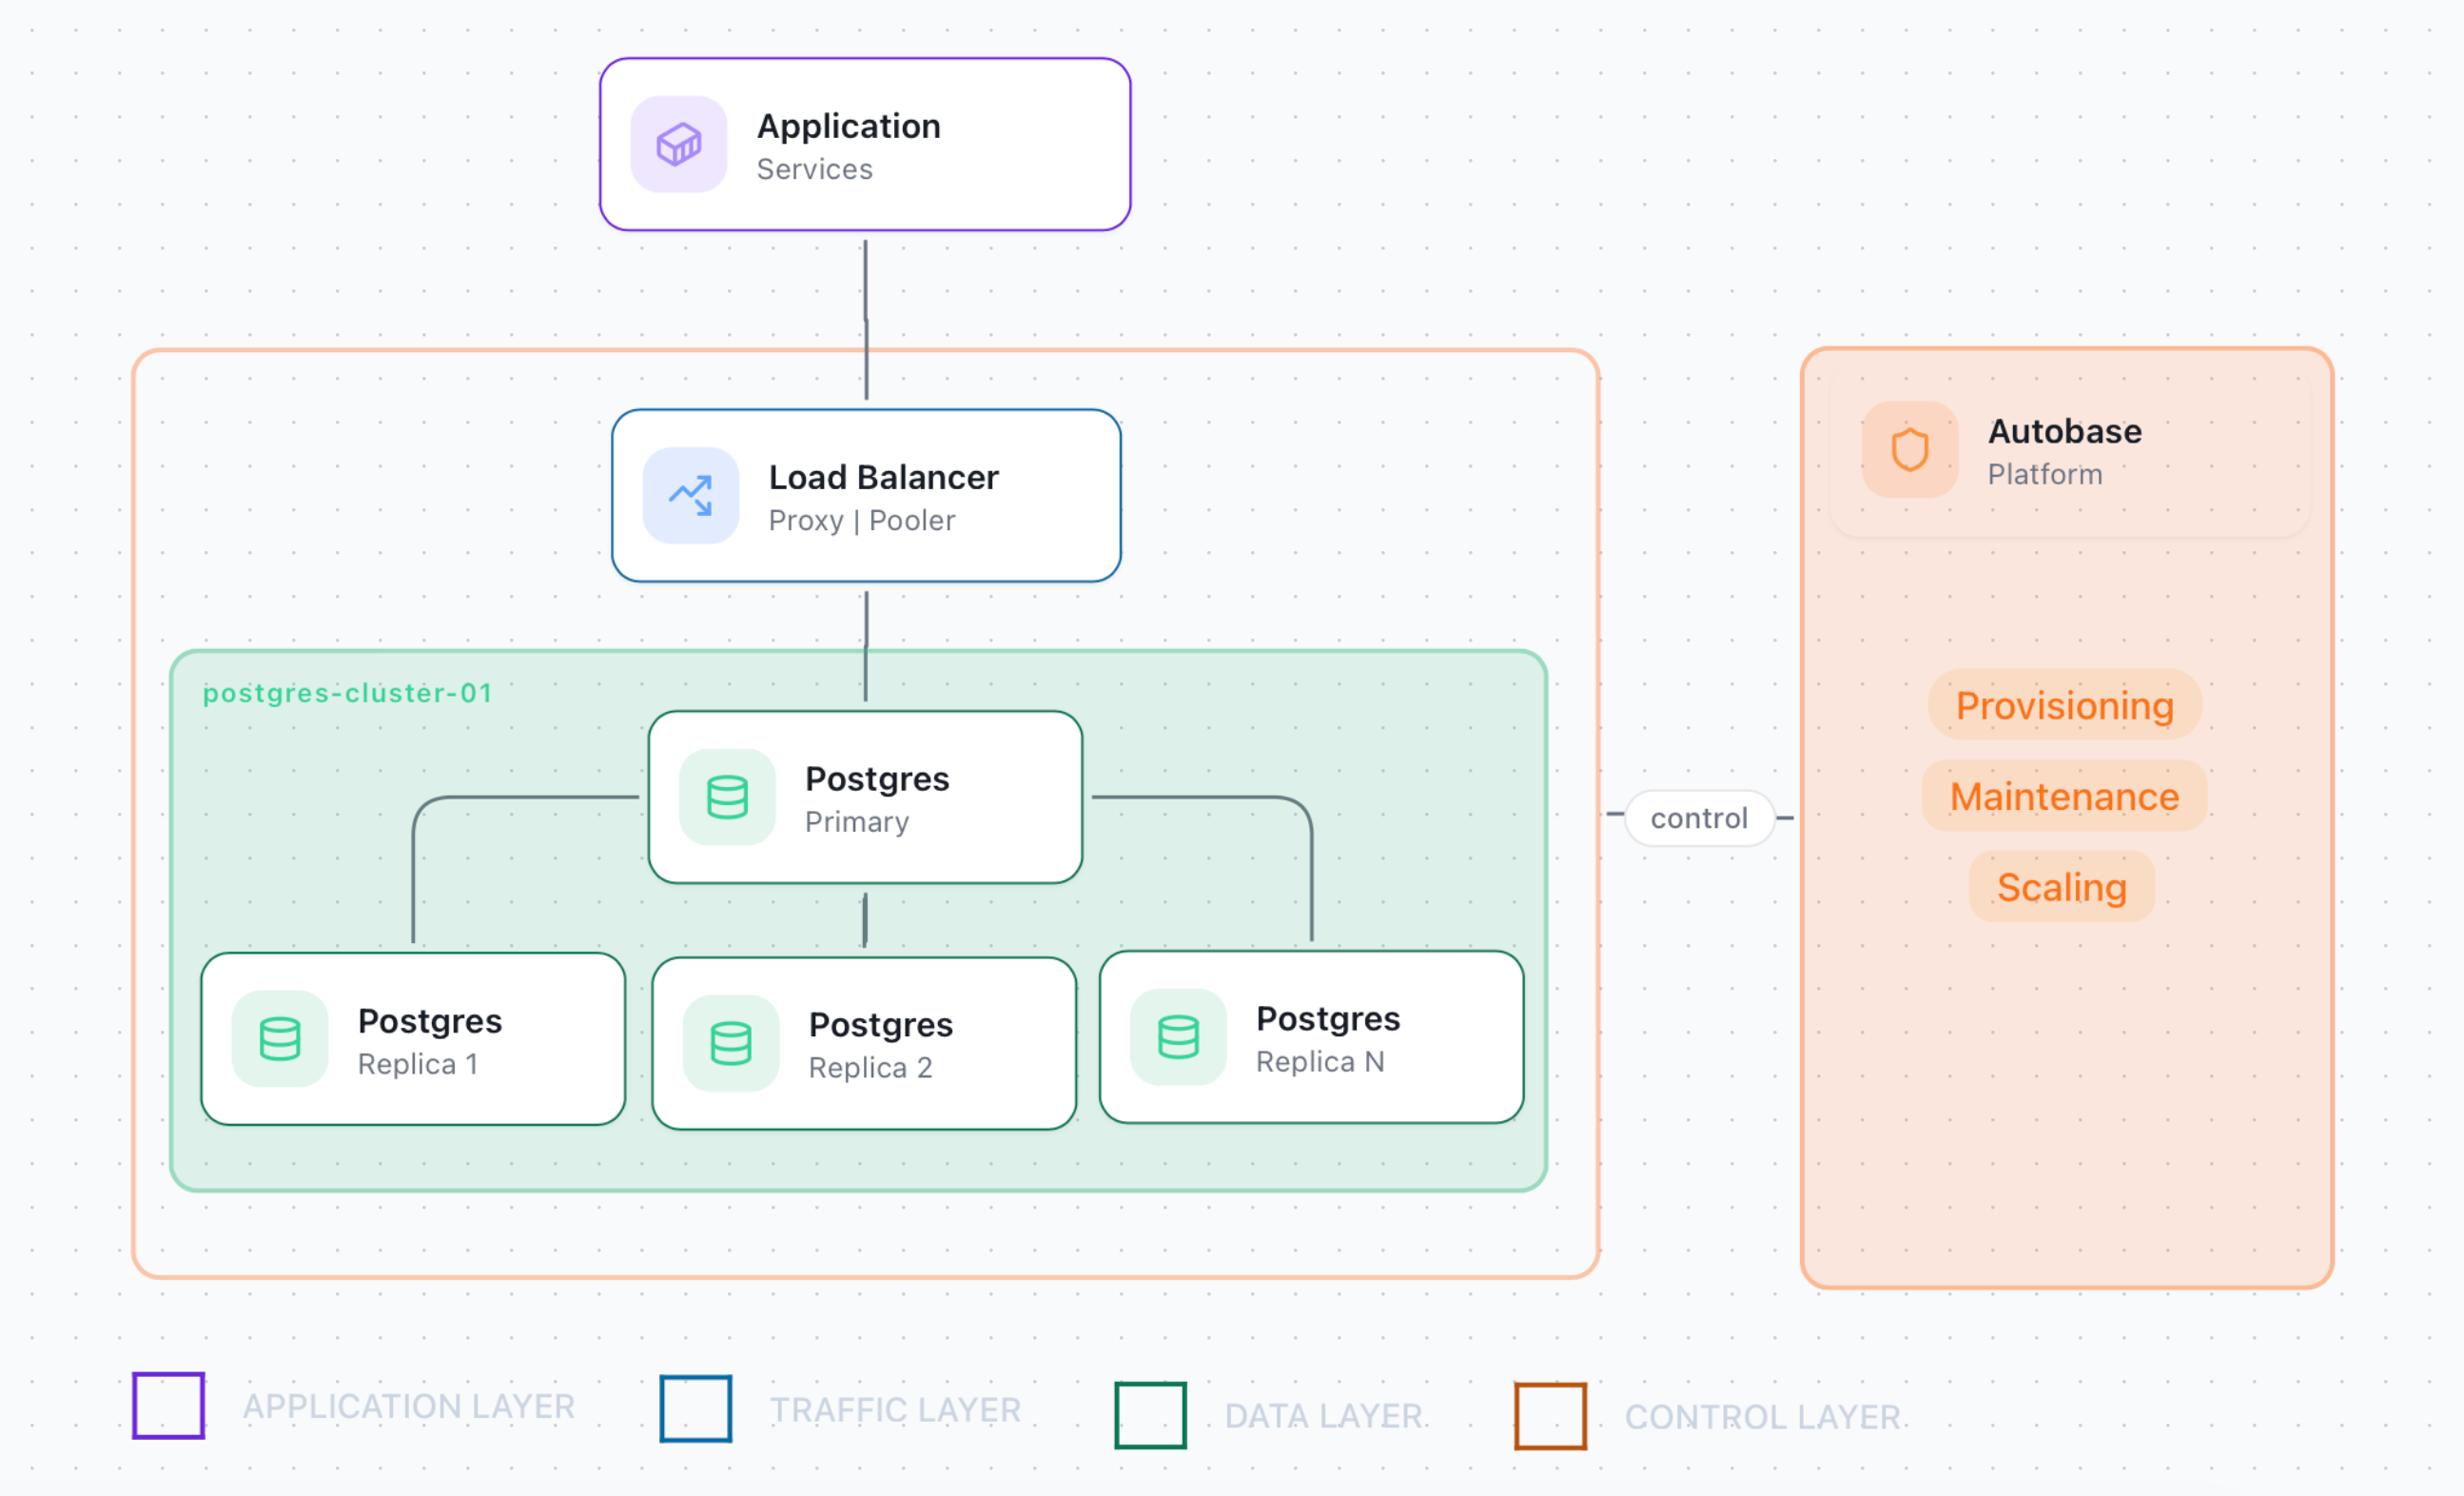
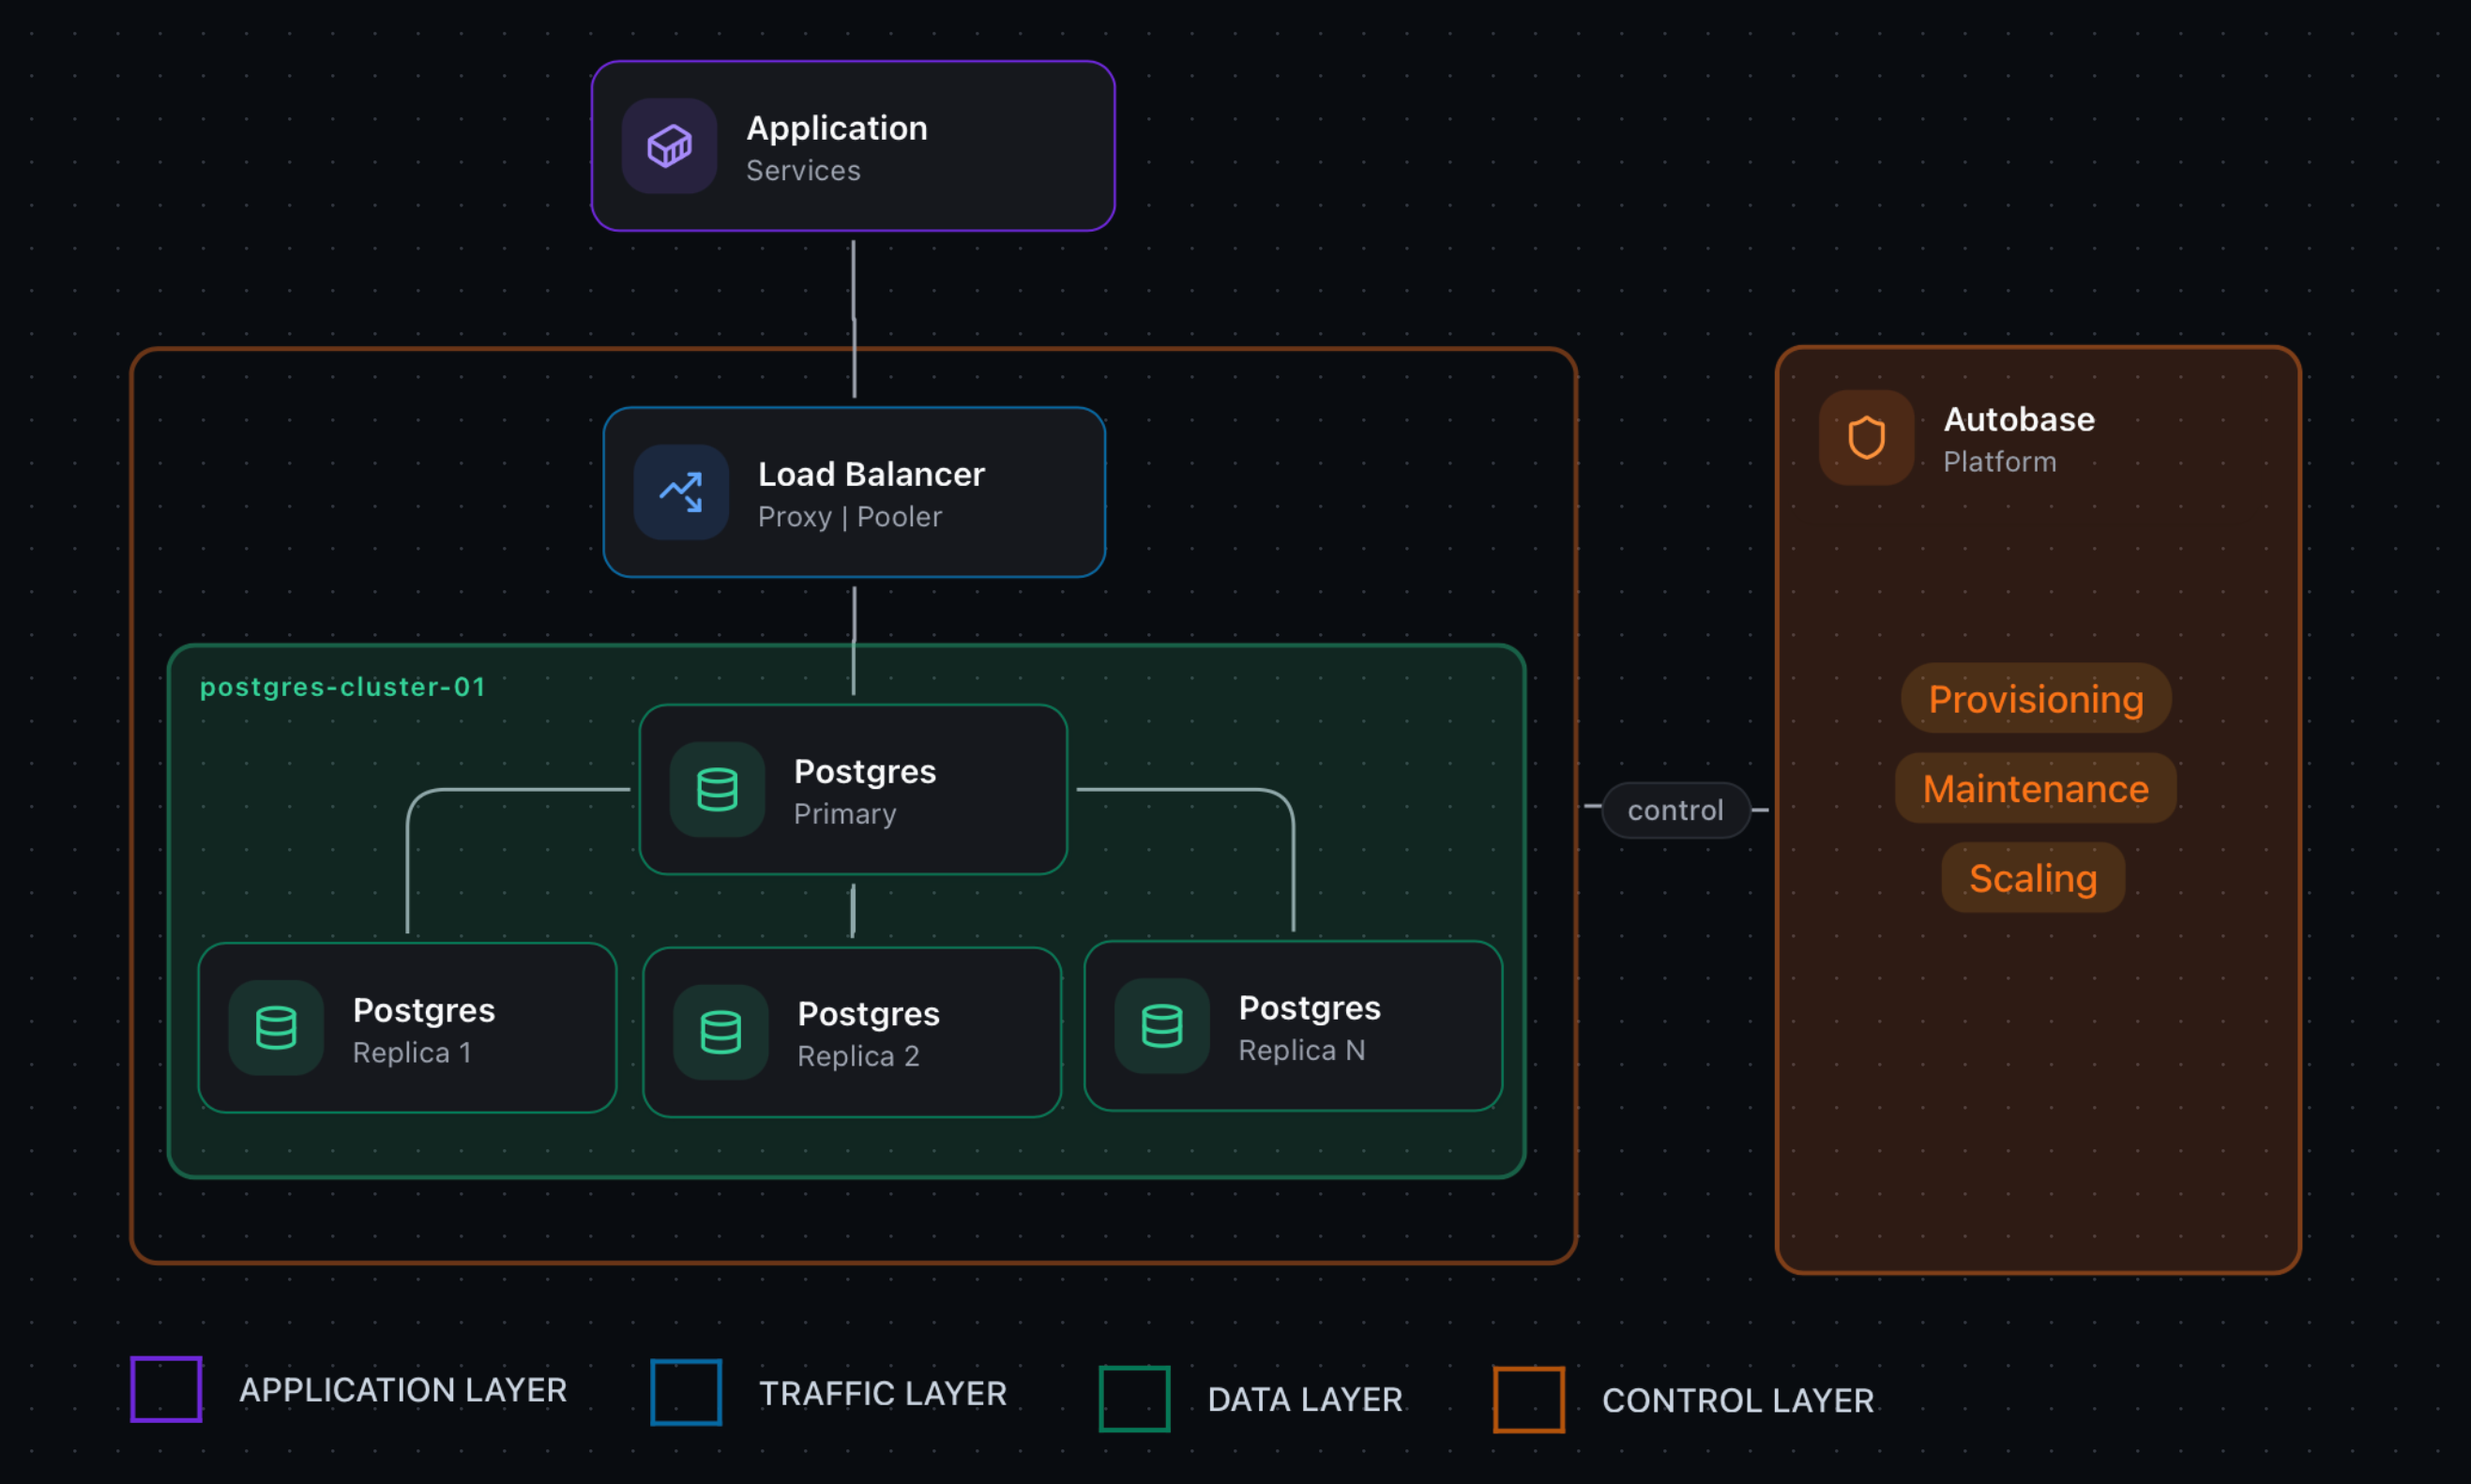
For a detailed description of the cluster components, visit the Architecture page.
Getting Started
Follow the step-by-step guide below to start the Autobase Console and create your first PostgreSQL cluster.
Review the Requirements section before deployment.
- Quick start
- Production setup
Use this quick start to try Autobase. For production deployments, we recommend following the Production setup tab.
Get the docker-compose file
curl -fsSL https://autobase.tech/platform.yml \
  --output ./docker-compose.platform.yml
Run the Autobase Console
docker compose -f docker-compose.platform.yml up -d
Open the Console UI
Go to http://your-autobase-server and complete setup.
Create a PostgreSQL cluster
Refer to the Deployment section to learn more about the different deployment methods.
This setup enables HTTPS with automatic certificate renewal and guides you through configuring unique secrets before the first launch. You will need a domain name pointing to your Autobase server.
Create a DNS record
Create a DNS A record pointing your domain to the Autobase server IP address.
Get the docker-compose file
curl -fsSL https://autobase.tech/platform.ssl.yml \
  --output ./docker-compose.platform.ssl.yml
Create a .env file
Create .env in the same directory as the Compose file. Set your domain and email address, and replace each secret below with a separate, unique random value:
DOMAIN=autobase.example.com
PG_CONSOLE_AUTHORIZATION_TOKEN=replace-with-a-unique-random-token
PG_CONSOLE_ENCRYPTIONKEY=replace-with-a-unique-random-key
PG_CONSOLE_DB_PASSWORD=replace-with-a-unique-random-password
Generate each secret separately, for example with openssl rand -hex 32. Default secrets are intended only for evaluation and must be replaced before production use or storing real credentials.
Restrict access to the file and do not commit it to Git:
chmod 600 .env
Set PG_CONSOLE_ENCRYPTIONKEY before storing credentials, back it up securely, and keep it unchanged across updates and restores. Changing it does not re-encrypt existing credentials and makes them unreadable with the new key.
These secrets are separate from the user credentials you create during the initial UI setup.
Run the Autobase Console
docker compose -f docker-compose.platform.ssl.yml up -d
Open the Console UI
Go to https://autobase.example.com (DNS name of your autobase server) and complete setup.
Create a PostgreSQL cluster
Refer to the Deployment section to learn more about the different deployment methods.
📩 Contact us at [email protected], and our team will help you implement Autobase into your infrastructure.